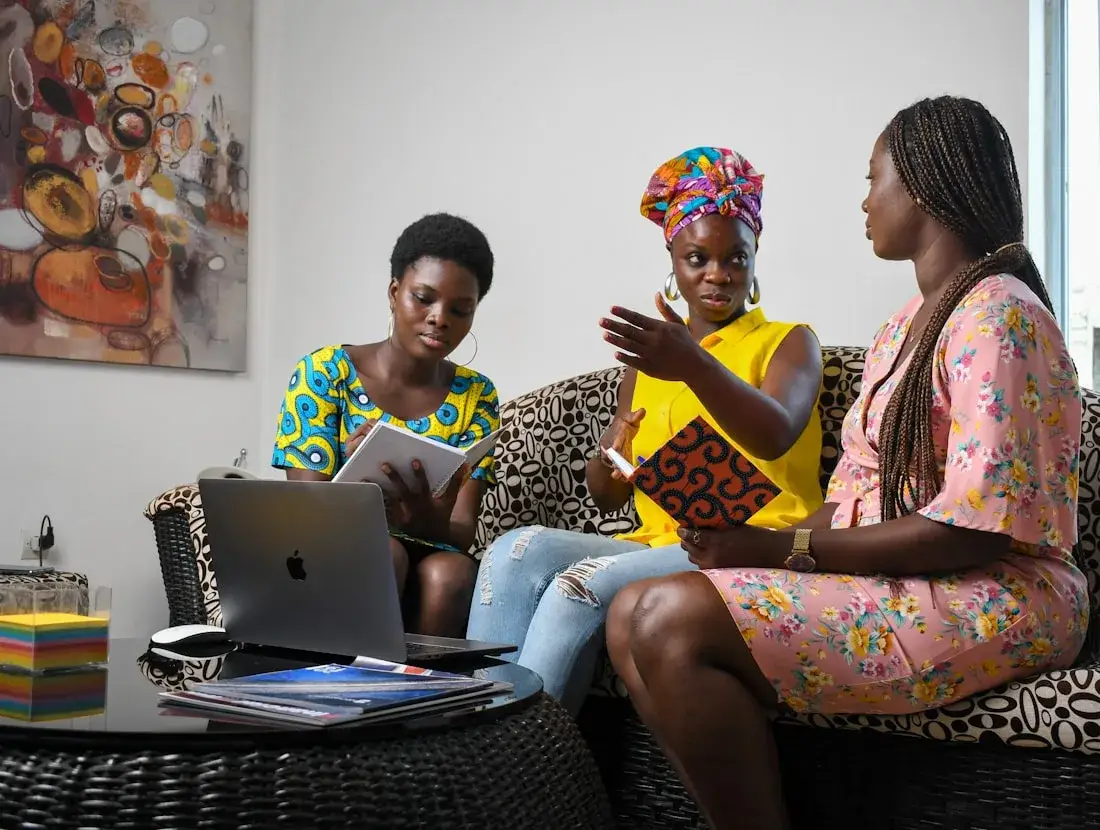
Beneficiary data usually lives on field tablets, personal phones and shared folders set up during a programme launch and never reviewed since.

An NGO working in Uganda may hold names, locations, household details, health status, biometric records and payment information for thousands of people who have no way to protect themselves if that data leaks.
That data usually lives on field tablets, personal phones, shared spreadsheets, messaging threads and cloud folders that were set up quickly during a programme launch and never reviewed afterwards.
Shared logins so any team member can submit forms. Personal devices carrying full beneficiary lists offline. Departing staff who keep access for months after leaving. Consent collected verbally with no record of what was agreed. And donor reports assembled from files nobody can locate a year later.
Donor compliance has moved well past a signed policy. Funders increasingly ask who can access beneficiary data, how it is stored, how long it is kept, what happens on a breach and whether staff have been trained. Institutions that cannot answer risk findings on audit and pressure at renewal.
The practical starting point is a data inventory. Know what you hold, where it sits, who can reach it and why you still need it. Almost every organization we speak to is storing data it no longer has any reason to keep.
Build a beneficiary data inventory
End shared logins entirely
Encrypt every field device
Offboard leavers within 24 hours
Record consent, do not just collect it
Set retention and deletion rules
Nakawa, Kampala, Uganda
Uganda and East Africa
Onsite and remote
John Doe joined UHA
12 people registered today
ECG Interpretation Workshop